Beyond the Safeguards: 5 Game-Changing Shifts in Ethiopia’s New Cybersecurity Proclamation
With the Critical Infrastructure Cybersecurity Protection Proclamation No. 1426/2026, Ethiopia has closed the book on informal, voluntary IT security practices. The legislation fundamentally reshapes how state enterprises and private entities manage digital risk, technology supply chains, and regulatory accountability.
Beyond standard compliance measures, five major legal shifts transform the national regulatory landscape.
1. Corporate Leadership and Tech Executives in the Crosshairs (Art. 25)
The most striking element of Proclamation No. 1426/2026 is its strict personal liability regime. Cybersecurity is no longer just an IT issue. It imposes criminal liability on corporate leadership.
- The Shift: Article 25 criminalizes standard compliance oversights. Missing report windows or using uninspected IT systems carries penalties up to one year in prison.
- The High-Stakes Provision: Major breaches causing service disruptions or national security harm trigger 7 to 10 years in prison. Even when such failures stem purely from negligence, the law prescribes 3 to 5 years of rigorous imprisonment.
2. A Statutory “Self-Sustaining” Cyber Fund (Arts. 11–15)
Regulatory mandates often face implementation hurdles due to resource constraints. Part Three addresses this directly by establishing a dedicated, permanent Critical Infrastructure Cybersecurity Fund.
- The Shift: Rather than relying on general government budget allocations, the law creates a permanent, self-sustaining financial mechanism.
- Capital Sources: The Fund receives mandatory contributions from critical infrastructure entities, service fees, and administrative fines.
- Earmarked Allocations: Collected funds directly support national research, capacity-building drills, public awareness, and critical system upgrades.
3. Supply Chain Pre-Clearance & Mandatory Inspection (Art. 7(12) & Art. 22(1)(f))
To mitigate third-party supply chain risks, the Proclamation restricts how organizations procure and deploy digital assets.
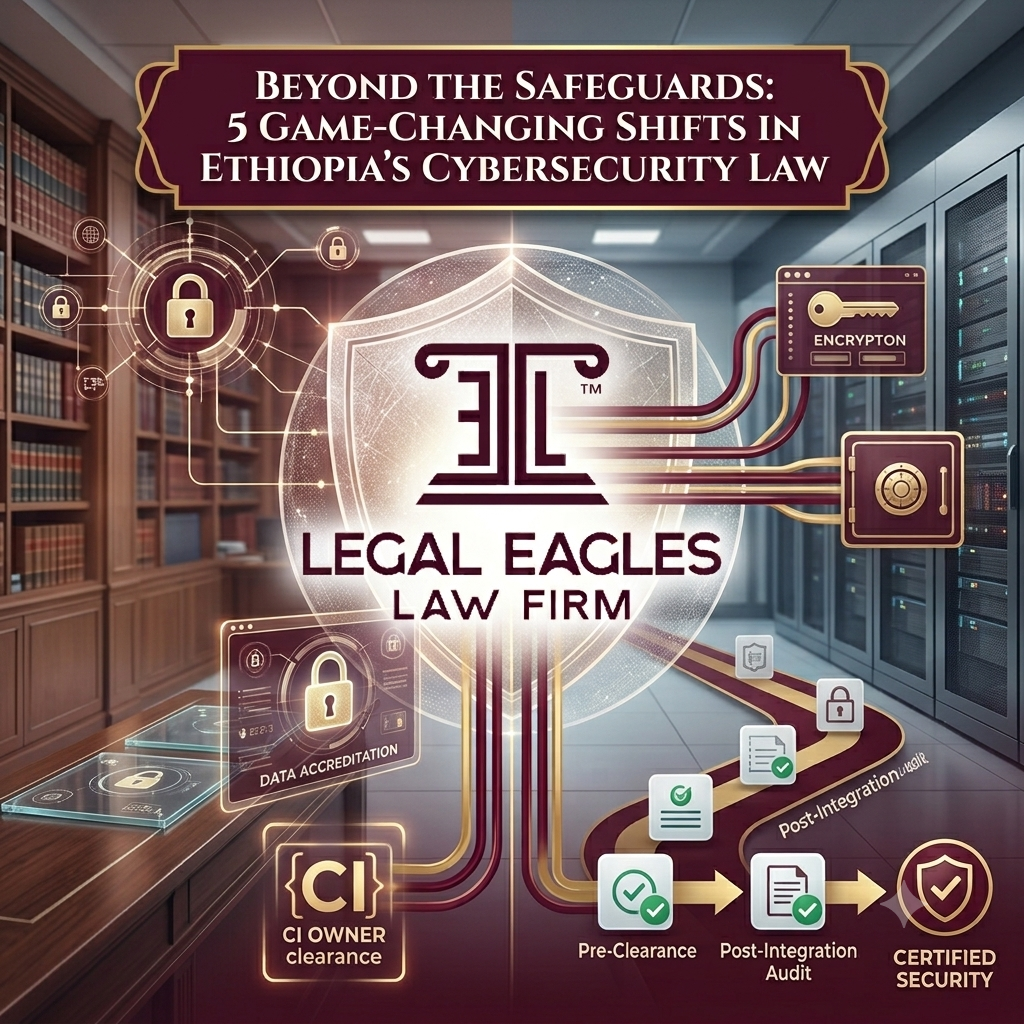
- The Shift: Institutions must obtain formal INSA clearance before deploying any new or upgraded system.
- Enforcement Penalties: Deploying uncertified systems triggers fines up to 1,000,000 ETB and criminal liability for officers.
4. Direct Gatekeeping of the Cybersecurity Market (Arts. 16–21)
The Proclamation establishes formal oversight for the commercial cybersecurity sector in Ethiopia, replacing informal vendor engagements with structured licensing.
- The Shift: Third-party providers cannot offer cybersecurity products, testing, or audits without an INSA license.
- Strict Licensing Criteria: Licensed vendors must maintain Ethiopian legal status, permanent local offices, minimum capital, and clean records.
- Mandatory Professional Accreditation: Individual cybersecurity practitioners working within critical infrastructure must hold recognized professional certifications.
5. Mandatory 48-Hour Incident Disclosure Benchmark (Art. 7(14) & Art. 22(1)(b))
Data breaches and cyber intrusions are often kept silent to avoid reputational exposure. Proclamation No. 1426 enforces transparency across both public and private sectors.
- The Shift: Infrastructure owners must report any detected cybersecurity incident to National CERT within 48 hours.
- Non-Compliance Costs: Suppressing breach details or ignoring National CERT instructions results in fines up to 2M ETB. Repeat violations trigger a fine equivalent to triple the maximum prescribed amount.
Key Operational Timeline
Per Article 28, the Proclamation enters into force exactly one year after its publication in the Federal Negarit Gazette. Institutions have 12 months to audit systems, update escalation workflows, and ensure all vendors are accredited.