When the Network Fails: Technical Negligence Under Ethiopia’s Electronic Invoicing System
Previewing “Technical Negligence” in a Digital-First Era
Under the rigid framework of Directive No. 1142/2026, the traditional excuses for delayed reporting no longer hold weight. Real-time transaction data must flow automatically to the state repository. Because of this, central tracking algorithms treat any transmission drop with immediate skepticism.
This creates a critical legal gray area. When is a network drop an unavoidable accident, and when is it “technical negligence”?
If a business fails to activate certified offline backup protocols during a network crash, regulators may penalize the gap as a failure of operational diligence. In the eyes of enforcement, using unvetted systems or failing to maintain continuous API alignment constitutes a compliance breach. The burden of proof shifts entirely to the taxpayer. To avoid catastrophic tax penalties, corporate entities must legally and technically prove that a transmission failure was entirely outside their control.
1. Introduction
Technology is seamless until it isn’t. Sudden internet blackouts, unexpected server crashes, and software glitches rank among the most disruptive moments for any modern business enterprise. Historically, internal IT departments quietly resolved these technical hiccups as temporary operational headaches. Under Electronic Invoicing Directive No. 1142/2026, a dropped network connection is no longer just a technical nuisance. It is an immediate legal risk. It is an immediate legal risk.
This directive replaces traditional physical cash register vouchers with real-time digital reporting. Transactional data must flow automatically from your ERP or point-of-sale setup to central state servers instantly.
But what happens when an outage blocks the digital highway? Connectivity failures or dropped API handshakes instantly trigger automated compliance flags on central tax servers. This introduces a high-stakes question for executives and investors: Where is the line between an infrastructure failure and punishable “technical negligence”?
2. Legal Risk of Silent Data Streams
To understand the legal exposure under Directive No. 1142/2026, one must first look at the digital mechanics governing the system. Legacy models rely on physical audits years after the fact, discovering data gaps slowly. Under the new electronic invoicing framework, however, the system monitors compliance continuously.
A corporate system glitch creates more than a Monday morning IT backlog. Because the system syncs transaction data to government repositories via secure APIs, a technical failure cuts off the data stream completely.
On the other side of that, API sits with an automated compliance algorithm. When a high-volume taxpayer’s real-time data stream suddenly cuts off or drops out of sync, the central servers do not assume it is a harmless internet outage. Instead, the system automatically triggers administrative red flags.
The immediate corporate consequences of these algorithmic flags are severe:
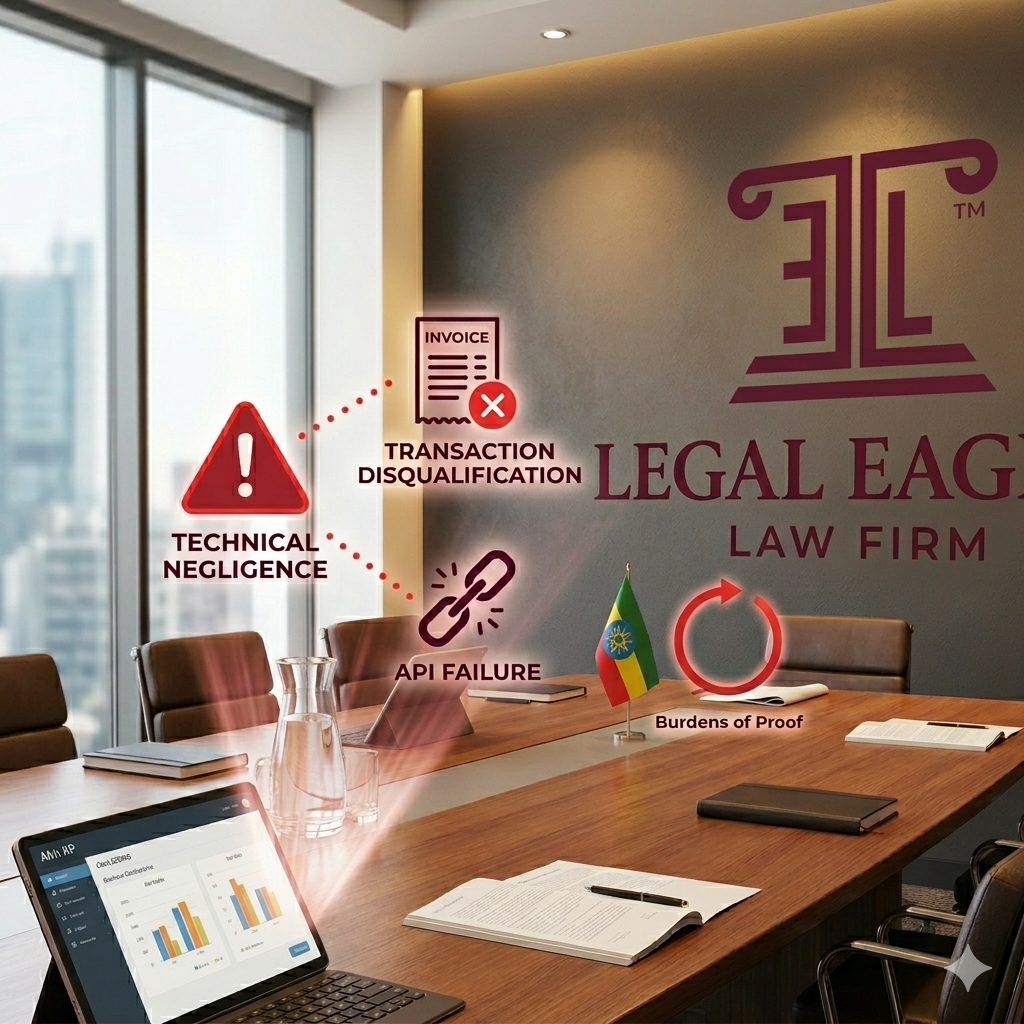
- Instant Transaction Disqualification: The tax authority risks flagging any transaction executed while the system fails to properly transmit data as invalid or unverified.
- The Sourcing Penalty Trap: The Ministry of Revenues may entirely disallow corporate income tax deductions and VAT input credits for any invoice your B2B corporate clients receive during a system failure. If your system glitch costs your client their tax deduction, it instantly shifts from an IT issue to a high-stakes client dispute.
- Immediate Regulatory Friction: Instead of waiting for an annual review, repeated or prolonged silent data streams can automatically bump a business into a high-risk taxpayer category, triggering targeted desk audits, administrative warnings, or immediate freezes on electronic invoicing privileges.
In short, when your data stream goes silent, the law views it as a potential compliance breach first and a technical failure second.
2. Defining “Technical Negligence” vs. “Force Majeure”
When a data stream to the Ministry of Revenues abruptly cuts off, the immediate legal question is one assignment: Who is legally responsible for the silence? To successfully defend against penalties under Directive No. 1142/2026, corporate taxpayers must understand the boundaries dividing an excusable infrastructure emergency from a severe compliance failure.
1. The System Malfunction Blame Game
- When an invoicing system fails to sync, it usually triggers an internal finger-pointing exercise between three distinct parties:
- The Third-Party Software Developer: Did the certified Enterprise resource planning or billing software vendor deploy an unstable patch or push a faulty update that broke the secure API handshake?
- The Internal IT Team: Did an internal system administrator accidentally alter database configurations, firewall parameters, or security certificates, effectively severing the transmission link?
- The State Infrastructure: Is the system failure a localized glitch or server outage on the Ministry of Revenues’ central API receiving end?
- Untangling this web requires clear legal framework agreements. Under the directive, the tax authority views the taxpayer as the primary gatekeeper. If your developer breaks the code, it is still your compliance failure until you legally recover damages through robust vendor indemnification clauses.
2. Infrastructure Failure: Maintaining Compliance Offline
In an ideal digital world, high-speed internet is an unblinking utility. Widespread connectivity drops, fiber cuts, and regional power failures are routine operational hazards.
Handling an infrastructure failure without losing your compliant tax status comes down to technical redundancy and automated software design. The directive does not expect businesses to stop selling the moment a network tower goes down; instead, it mandates that authorized billing systems switch seamlessly into a secure, tamper-proof offline queueing mode.
To maintain baseline compliance during a network blackout, a business must ensure its systems are actively:
- Encrypting and locally time-stamping every invoice generated during the drop.
- Prevent manual backdating or tampering with database values while offline.
- Utilizing secondary network failovers (such as a backup cellular data link or a secondary ISP) to attempt automatic re-transmission.
3. Shifting the Burden of Proof: Proving Good Faith
Perhaps the most striking legal shift introduced by this real-time digital architecture is the complete reversal of proof burdens. In a traditional tax dispute, the authority must investigate and demonstrate non-compliance. In the automated environment of Directive No. 1142/2026, the central server flags the data drop instantly, rendering the taxpayer “guilty” of a compliance interruption until proven innocent.
If your system goes silent, you cannot simply claim the network was down. Corporate entities must proactively compile an indisputable technical trail to prove they acted in good faith. This means maintaining automated, verifiable system logs that register exact API error responses, telecom network uptime reports, and internal software diagnostic data. When the network fails, your technical logs serve as your primary legal defense.
IV. Strategic Safeguards: Protecting Your Practice Before the System Crashes
Mitigating the legal risks of a real-time digital tax infrastructure requires a deliberate strategy that combines robust technical redundancy with tight legal protections. To insulate your business or your clients from accusations of technical negligence, you must implement the following strategic safeguards immediately:
- Incorporate Strict IT Vendor Indemnification Clauses: When negotiating or updating software service agreements with certified ERP or billing system vendors, do not rely on standard, off-the-shelf Service Level Agreements (SLAs). Contracts must include specialized legal language that holds the technology vendor financially and legally liable for compliance disruptions caused by software-side glitches, unvetted patches, or failed API updates.
- Deploy Localized, Tamper-Proof Offline Queues: Ensure you design your technical infrastructure to switch instantly to an authorized offline mode the moment a connection drops.
- Establish Multi-Network Redundancies: Eliminate single points of failure within your internet infrastructure. Businesses should maintain a primary fiber or broadband line paired with an automated cellular data failover or a secondary, independent Internet Service Provider (ISP) to ensure continuous data transmission during localized network drops.
- Maintain Automated, Audit-Ready Technical Logs: Because the burden of proof shifts to the taxpayer during a data stream interruption, your IT systems must generate immutable error logs. These logs should capture exact network response codes and internal diagnostics, serving as your primary, verifiable evidence to prove good-faith compliance during an infrastructure failure.
Ultimately, the transition to a real-time digital tax ecosystem transforms technical infrastructure into a core pillar of regulatory compliance. Under this new digital paradigm, an enterprise can no longer afford to treat network dropouts or software